Whoa!
Okay, so check this out—I’ve been living in the crypto world for years, and somethin’ about private keys still gives me pause. My gut said hardware wallets were the answer, but then I started using smart-card designs and things shifted. Initially I thought they were just gimmicks, but then the convenience and the security model actually changed my workflow, and not in a small way. Honestly, this is a weird mix of relief and mild paranoia all at once.
Really?
Here’s the problem: private keys are fragile, and most people treat them like passwords when they’re not. People write seed phrases on paper, stash them in a drawer, or memorize stuff and then forget—this part bugs me. On one hand you want absolute isolation; though actually when you force too much isolation you make human error inevitable. So the question becomes practical: how do you keep keys both secure and usable without turning into a paranoid fortress dweller?
Hmm…
Smart-card wallets answer that by changing assumptions; they treat the key as a physical object that never leaves a tamper-resistant element, and that matters. In practice, that means your signing key sits in a chip and the phone or reader only sees signatures, not the secret itself. My instinct said “this is overkill,” yet every time I recovered from a phone wipe or managed teammate access, the card-based flow was cleaner. I’m biased, but for some users it’s the best compromise between security and everyday usability.
Whoa!
The tech is simple-ish at the concept level but subtle in execution: secure elements, NFC taps, firmware that refuses to export a key, and deterministic wallets that let you manage multiple addresses without exposing secrets. For developers and security folks there are lots of edge-cases—timing attacks, supply-chain risk, and counterfeit hardware—but for most users the biggest wins are anti-phishing and reduced attack surface. Actually, wait—let me rephrase that: the biggest win is avoiding the two big human failure modes, accidental deletion and credential theft. So yeah, the design flips the script by minimizing what humans have to do wrong.
Seriously?
Okay, so check this out—I’ve used a few smart-card solutions and one that stood out was the tangem wallet for its card form factor and straightforward user flow. The thing I liked was tapping the card, signing a transaction in plain sight, and moving on—no cables, no seed file scattered across devices. On the other hand, the card approach forces you to think physically about backups; if you lose the single card you need a reliable recovery plan, and that’s a real behavioral challenge. (oh, and by the way… I once left a backup card in a gym locker—true story, don’t do that.)
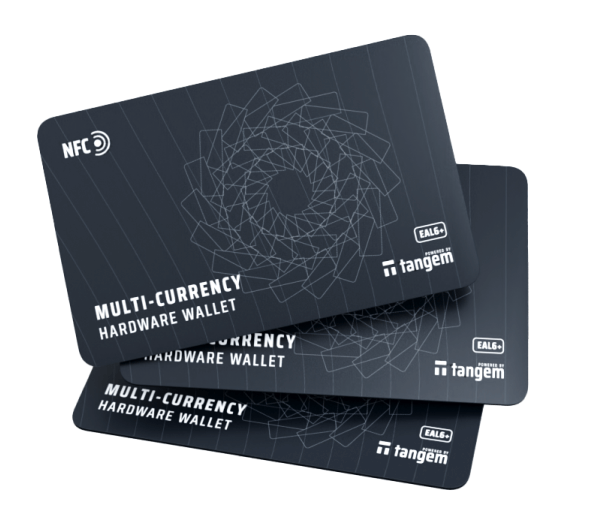
How smart-card wallets protect private keys
Wow!
First, there’s the secure element: a microchip certified to resist tampering that stores the private key and runs the cryptographic operations internally. Then, you have the interface model—NFC or contactless signing—where the host device receives only signatures and prompts, which drastically reduces the host’s ability to steal the key. Initially I thought full air-gapped setups were strictly safer, but in the wild people misconfigure them; smart cards reduce user error while keeping a high security baseline. On top of that, some cards incorporate anti-cloning measures and attestation, which helps verify authenticity before you trust them.
Whoa!
There are tradeoffs though, and I’m not 100% sure about every vendor claim, so you have to vet supply chains and firmware practices. My working rule is: trust but verify—look for independent audits, visible attestation flows, and a recovery philosophy that fits how you operate. On one hand you get a frictionless tap-and-pay vibe; on the other hand you must plan for loss, physical damage, or obsolescence. In short, the device simplifies some risks while introducing others, and users need to think about that balance.
Hmm…
Usability is underrated in security conversations because if a system is too hard, people will circumvent it in clever and dangerous ways. Smart-card wallets win here by being simple—tap, confirm, done—so adoption friction drops and safe behavior increases. I’m biased, but design matters almost as much as cryptography for everyday users; the easier the secure option, the less likely people are to copy-paste seeds into email or cloud notes. That said, convenience should never be an excuse for skipping backups or ignoring recovery procedures.
Whoa!
Threat modeling matters: think targeted attacks, supply-chain tampering, and social engineering. Cards help a lot against remote malware and phishing because an attacker rarely gets a physical tap, but they do little against coerced disclosure or a bad backup that was photographed. So, your defenses should be layered: physical security, good backup hygiene, and strong passphrase policies for additional protection. Something felt off about relying on one layer alone, and that’s why multi-layer planning is very very important.
Really?
Adoption is slowly picking up because the UX hits the right notes for mobile-first folks; people who carry their phone already accept NFC taps for payments, so the mental model is familiar. On the other hand, enterprises might balk at single-card workflows without robust key recovery and multisig integrations, though there are hybrid approaches that combine smart cards with custodial or multisig setups. Initially I thought enterprises would ignore cards, but then I saw teams using them for signer roles combined with policy-driven redundancy, and that changed my view.
Whoa!
I’m not saying smart cards are the final word; they’re one very practical tool in a broader toolkit of key protection strategies. If you’re managing modest holdings and crave simplicity, they can be transformational. If you’re securing institutional flows, think multisig with distributed cards and audited firmware, and keep legal and operational controls tight. My instinct said “go all hardware,” but in reality the right answer depends on context, threat model, and how much you trust the supply chain.
FAQ
Are smart-card wallets safe for everyday users?
Yes—when used properly. They remove many common attack vectors by keeping the key in a secure element and only exposing signatures to hosts. That simplicity reduces user mistakes, though you still need a reliable backup and to verify the card’s authenticity before trusting it.
Which smart-card wallet should I consider?
For a card-style experience that balances usability and strong key protection, consider the tangem wallet. I’m not affiliated, and I’m not claiming it’s perfect, but it’s a practical option that demonstrates how this form factor can make secure crypto management feel natural.
Hmm…
I’ll be honest: the technology isn’t magic, and humans still make the final call on security. So take a breath, plan a recovery strategy, and pick tools that match how you live and work. On balance, smart-card wallets are a pragmatic step forward for people who want solid protection without living in a bunker. This part excites me, though I worry about complacency; keep learning, and keep your backups safe…